The deliverable
The report is what you keep once the testing is done, so it gets real attention. Every engagement is written up in the same structure, meant to work for the executive who signs off, the engineer who fixes it, and the auditor who reviews it later.
Each engagement concludes with a formal written report comprising an executive summary and a detailed findings section. Every finding is assigned a severity rating, documented with the steps and evidence needed to reproduce it, accompanied by specific remediation guidance for the responsible team, and presented in order of risk.
Following remediation, we retest the reported issues and issue a revised report suitable for distribution to clients and auditors. The covers below illustrate the format used for web application, internal network, and mobile engagements; a complete sample report is available on request.
Hover for findings, click to enlarge.
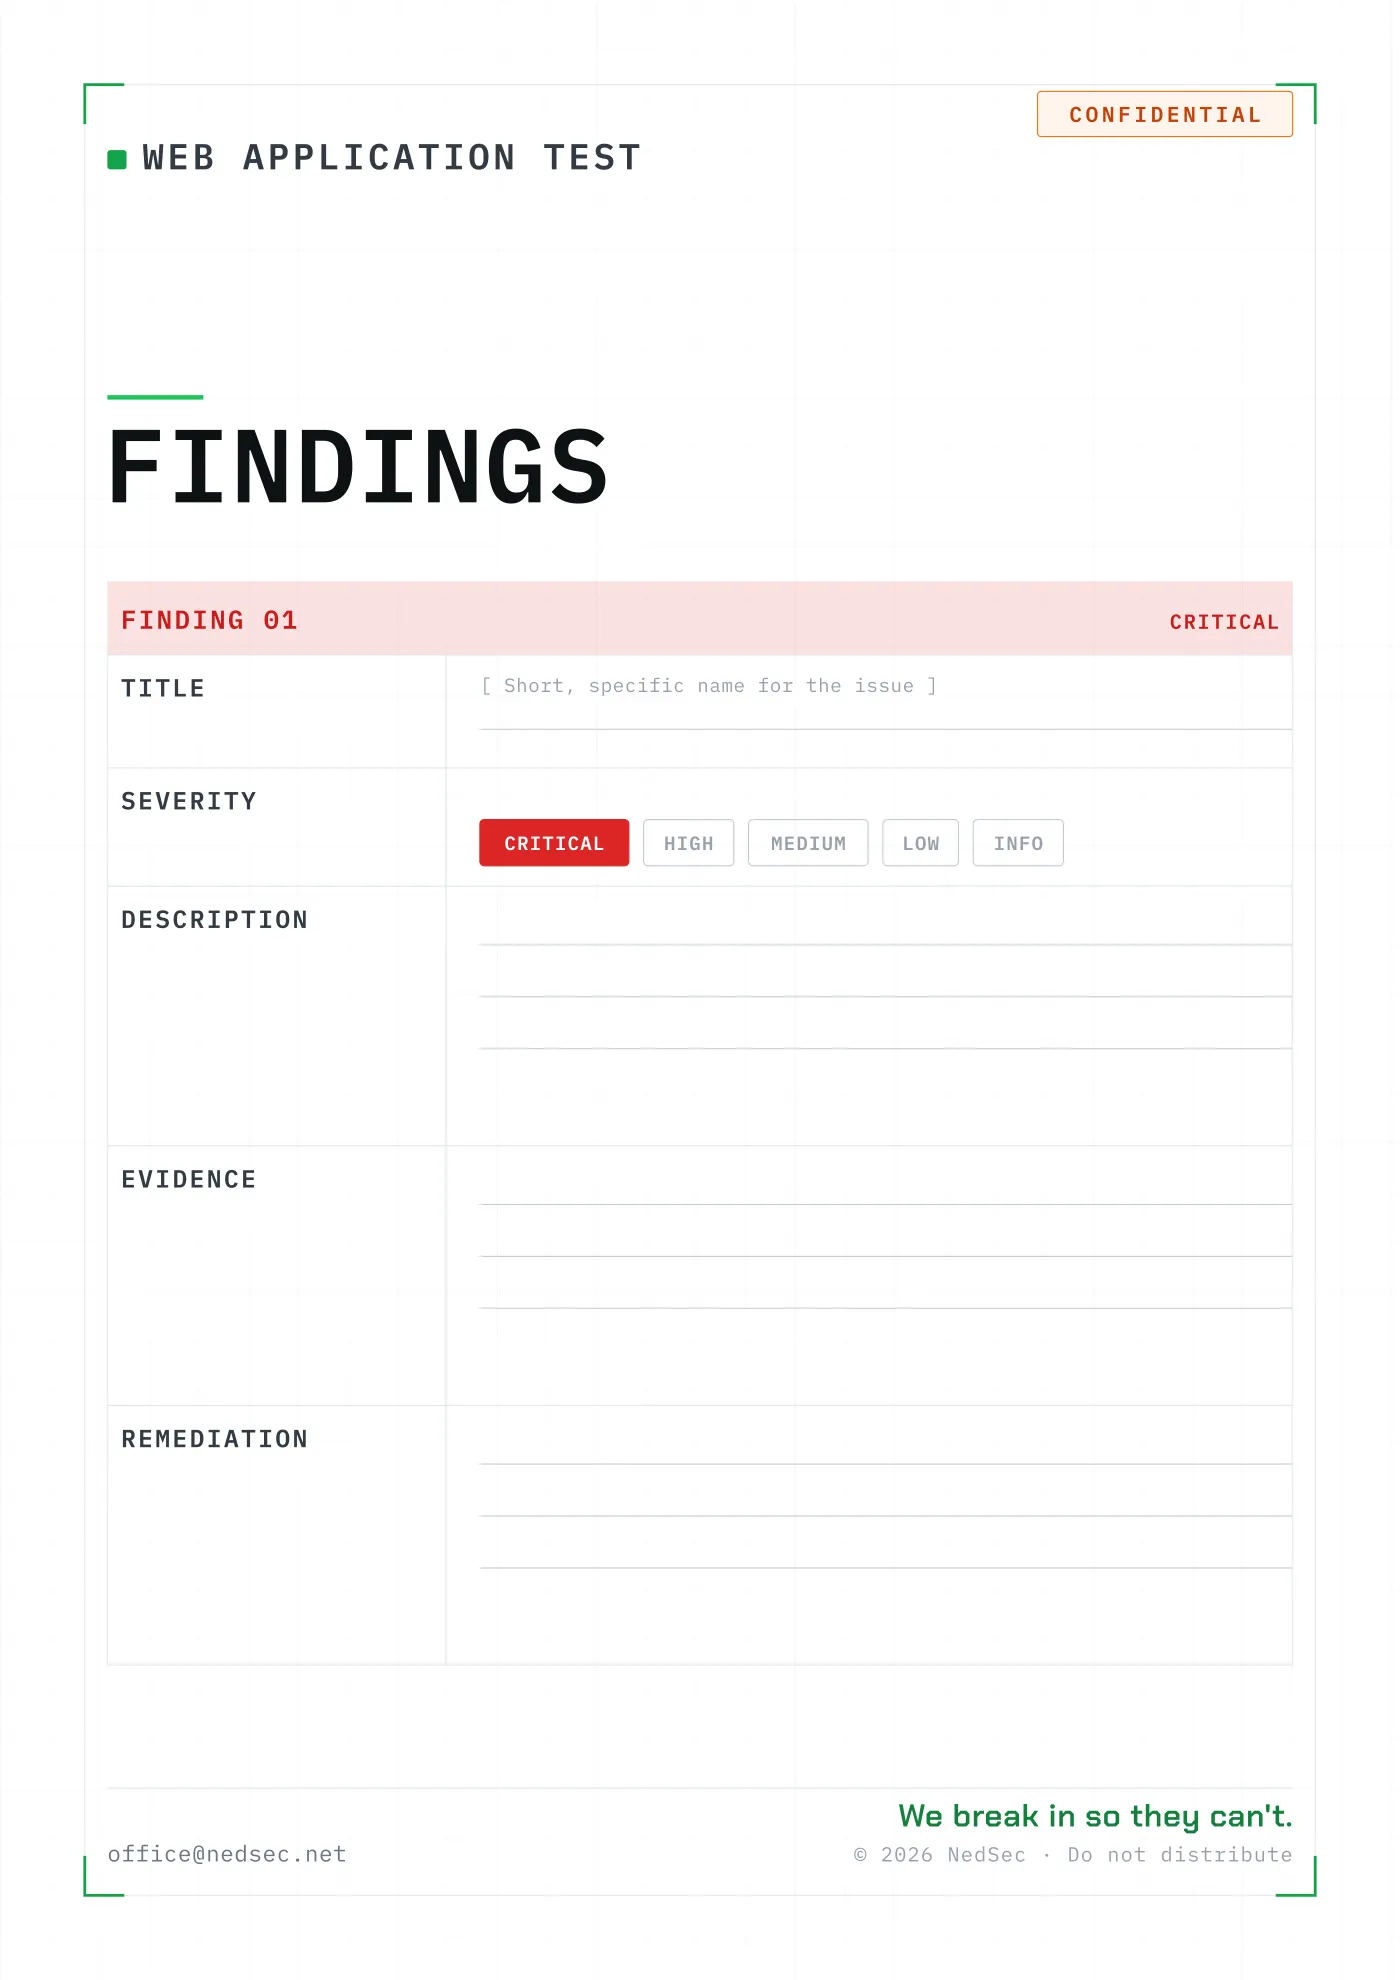
Web application test
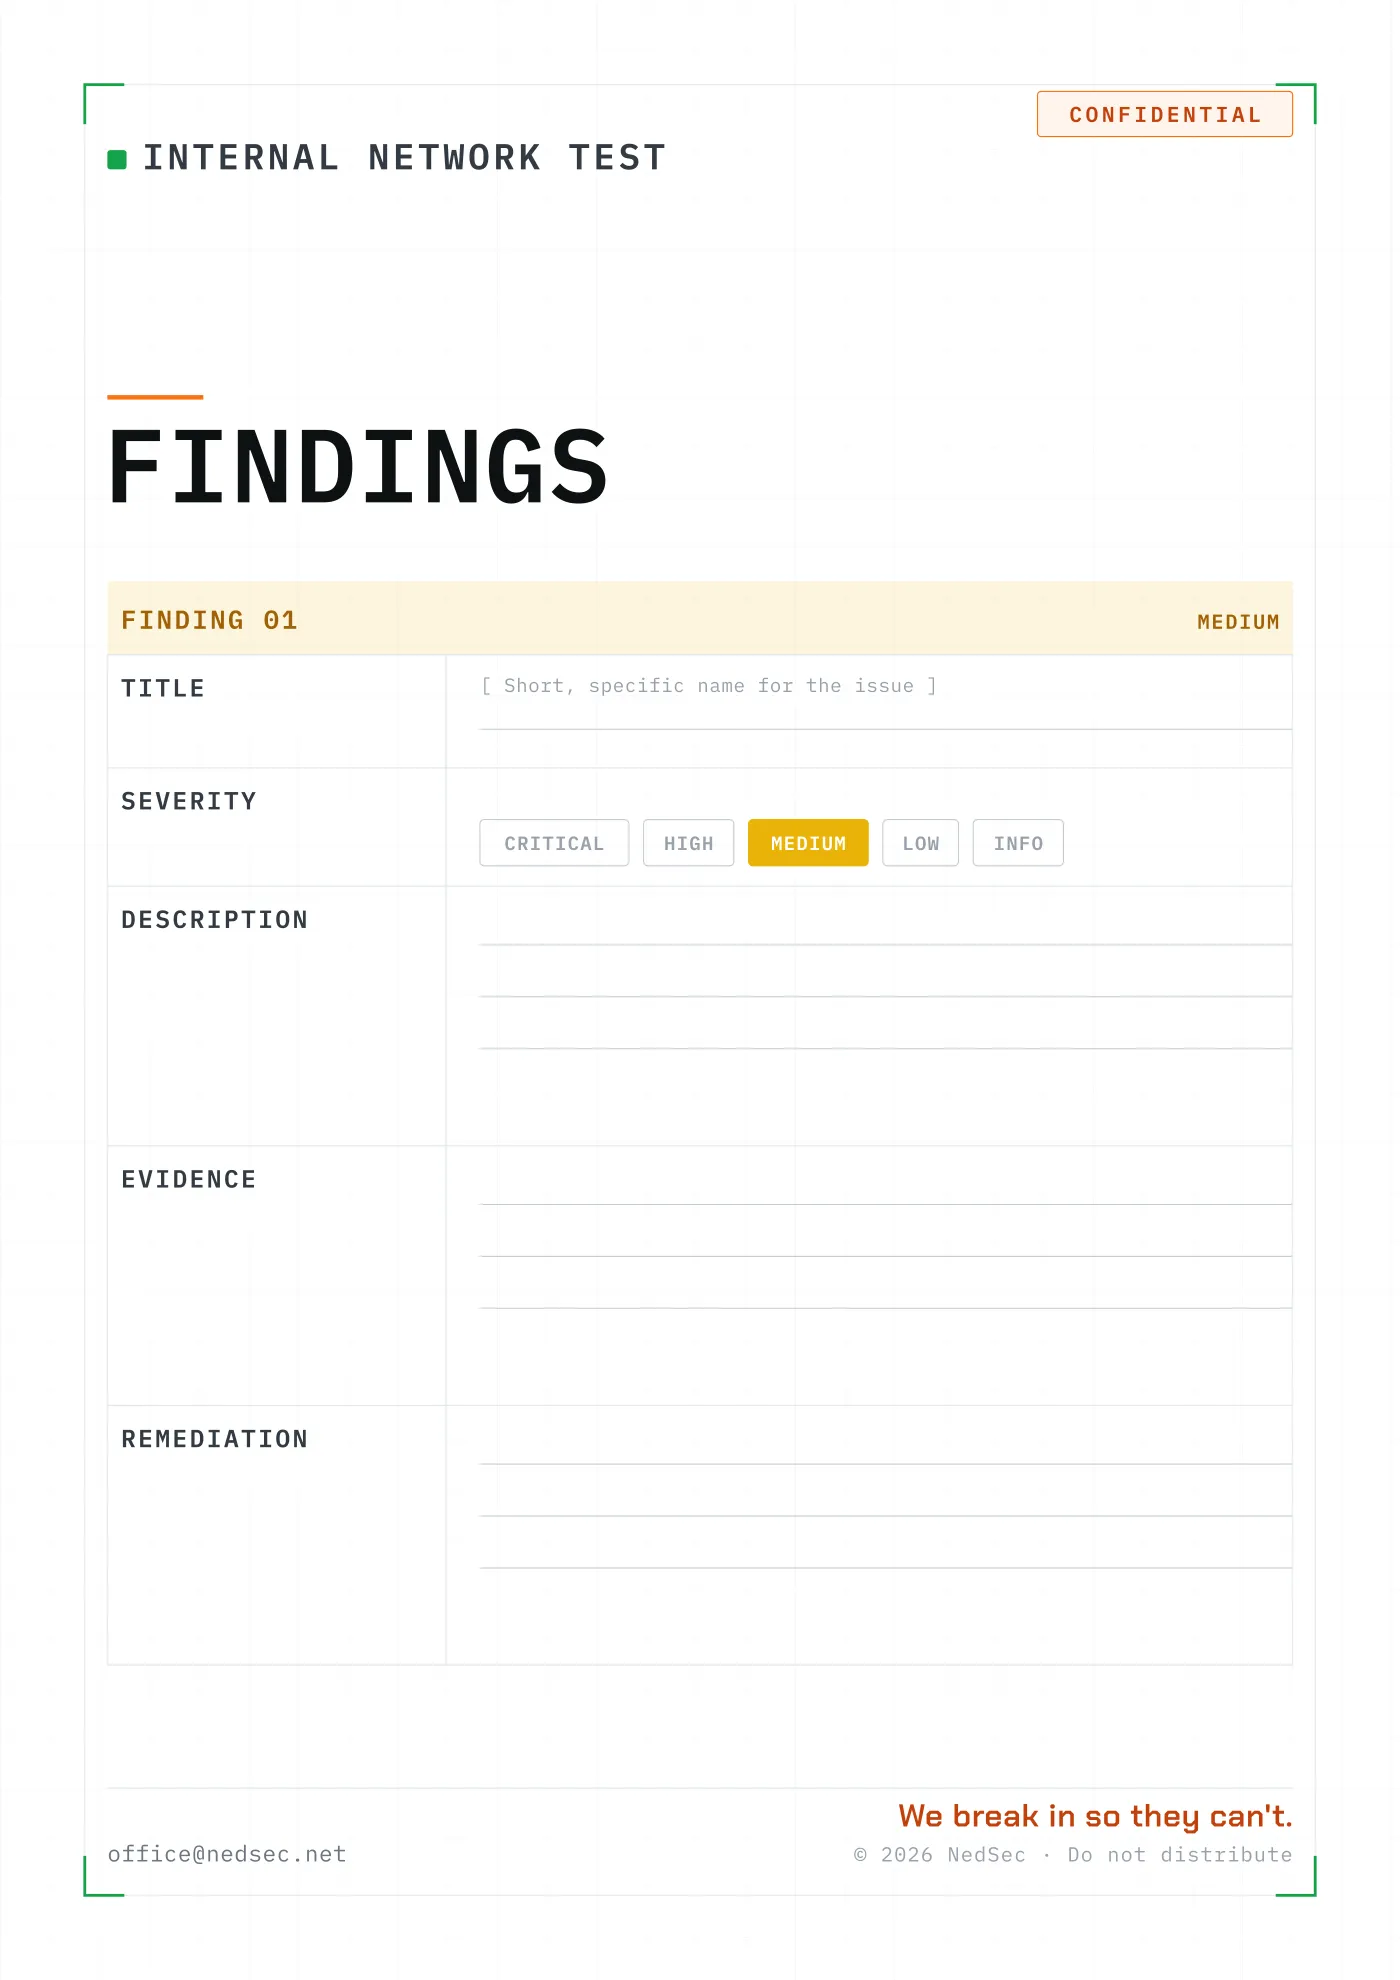
Internal network test
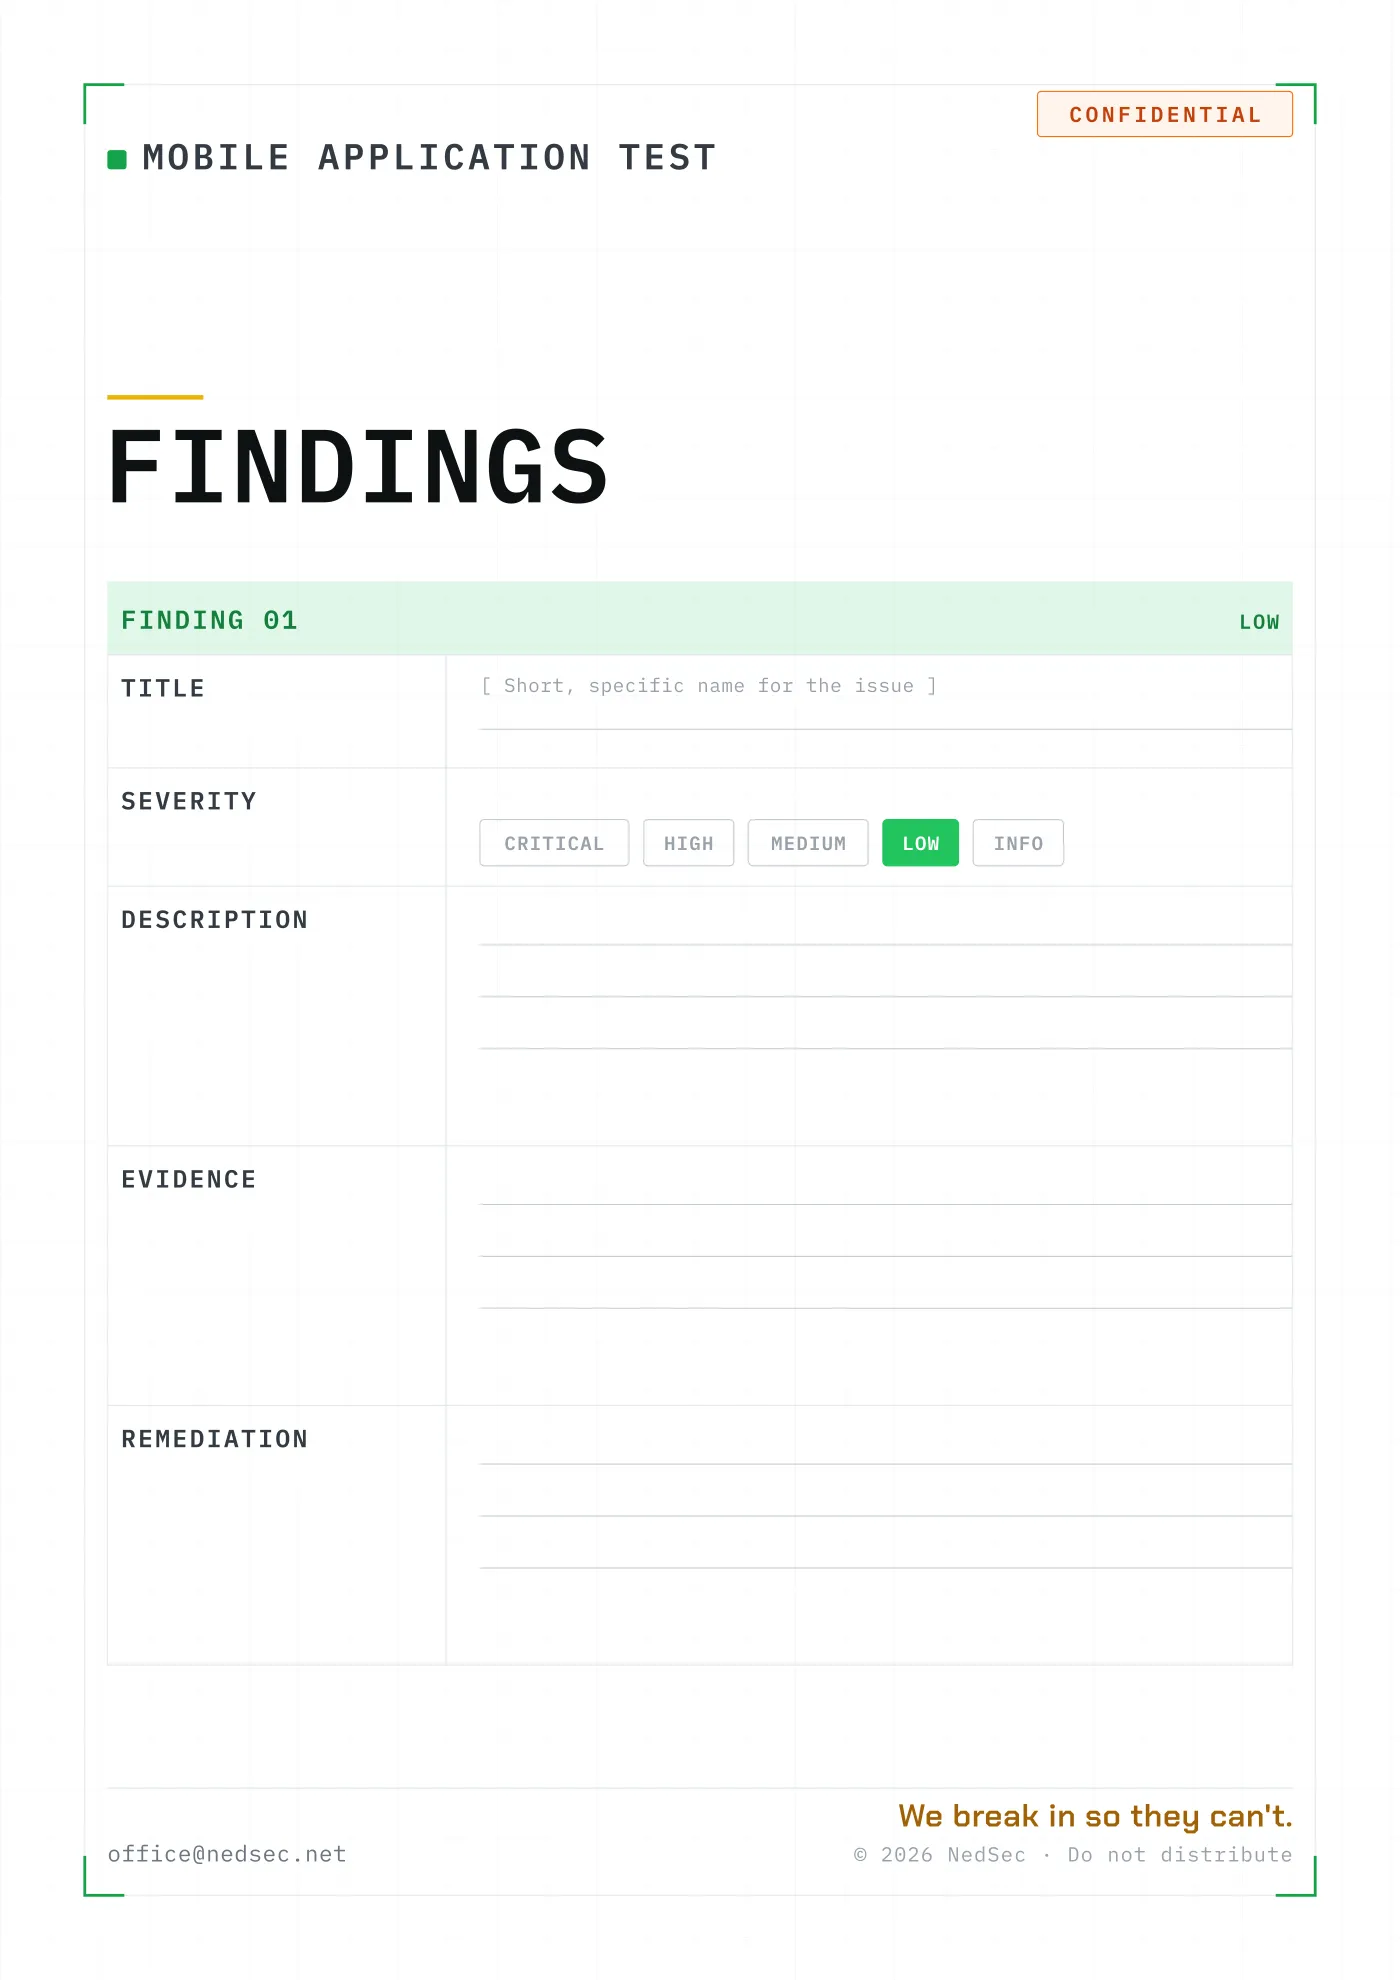
Mobile application test